Yahoo! Messenger web cache found + more updates + 0.6.0 development progress
Hi buddies!
We have managed to acquire web cache from a build of Yahoo! Messenger 6.0 (dated ~2004/2005) containing Yinsider configuration files, some IMVironments, and some audibles from the ZN/TW regions. We have uploaded them to the Internet Archive, and we will be implementing them into CrossTalk with the 0.6.0 update. Huge thanks to EternalQuest for finding all of this stuff!
Speaking of 0.6.0, it is coming along quite nicely. We're expecting to release it later in Spring.
We're also proud to announce that 0.6.x will be the first release series to be fully open source! Some time after 0.6.0's release, the source code to all services and components that make up CrossTalk will be released. We will not be re-using the existing repoistories due to hardcoded API keys et cetera; we will instead be creating new ones which will be used from that point forward.
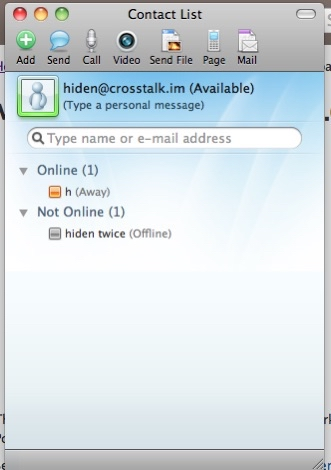
So far we have implemented the alias system (using @crosstalk.im as your e-mail inside MSN instead of your personal e-mail), logging in with usernames on MSN Messenger 1.0, many AIM changes (instant messaging, buddy list management, fixing the server crash that caused it to be disabled, and more), Confrences in Yahoo! Messenger, started work on supporting Messenger:Mac, and began work on implementing the MySpaceIM protocol. Here are demos of some of those features:
We've also made several updates to 0.5.x (the current production codebase) here are the changes since the last blog post (0.5.19 - 0.5.22):
- Security: Fixed passwords being logged base64-encoded in INS logs when user changes password (not during registration). We have fully cleared the logs so these are no longer stored on our servers. We can also assert that there has been no unauthorized access to the data and there should ideally be no security risk, but we do not discourage you from changing your password anyway if you feel it is necessary
- Security: Fixed the error messages for account lookup and password verification failure being different, which could allow indication of valid users
- General: Began a code cleanup across the board that will continue into 0.6
- General: Logging into CrossTalk with a restricted e-mail address (@crosstalk.im and other CrossTalk-related addresses, temp mail domains, and Escargot/NINA addresses) is no longer allowed, you are prompted to change your e-mail address before you can log in
- Operations: Added a proper contact e-mail address for CrossTalk's team rather than using the lead dev's personal e-mail address
- Operations: Added the ability to disable logins from people who have not updated their patches (connecting from the .xyz domains), which will display an alert/system message linking to a guide on how to update them. This will be enabled on the production service in the future
- Database: Stats DB is now compatible with MySQL (buggy, particularly with the online users counter, production still uses SQLite)
- MSN: Fixed a bug in the Mess.be Tetris game that could cause client crashes
- MSN: The 'Read the Messenger team blog' link now correctly links to this blog
- MSN: For client devs, MSNP2-based (MSN Messenger 1.0 etc) clients will now use the MD5 authentication scheme by default. CTP is still available but NOT recommended
- MSN: PocketPC clients should no longer fail during challenges
- MSN: Fixed the user storage domain in the GetProfile SOAP response, roaming display pictures should now work
- MSN: MSN's connection troubleshooter should no longer report a Key Ports error if there are no connection issues
- Yahoo: Fixed session crashes when sending a photo/file sharing invitation on newer versions (not implemented yet)
- Website: Re-added the Server Status page due to our UptimeKuma instance being shut down
- Website: Refactored the backend code for the Downloads pages
- Website: Redesigned the Password Reset/Changing pages
- Website: Redesigned the Stats page
- Website:: Redesigned the member directory table to make it more readable, and also to make it work properly on mobile
- Website: Updated some strings to be more user friendly, part of the ongoing UX efforts
- Website: Temporarily removed the image from the home page as it shows AIM, we don't feel right advertising it at the moment as it's disabled on the production service
- Website: INS host and port are now configurable in settings
- Website: Updated the FAQ to remove mentions of ProxHTTPSProxy (due to it no longer being functional), add a section about false positives, and some other changes
- Website: Updated the TOS page (the TOS itself was not updated)
- Website: Fixed login redirects not working properly, before it would always redirect to Account Settings no matter which page triggered the lock. Now it'll redirect to the locked page, and will redirect Account Settings no page triggered it (i.e. logging in via the Log in button)
- Website: Rewrote the Blog's RSS feed to use PyRSS2Gen, should fix issues loading in feed readers/browsers
0.5.22 will be the final version in the 0.5.x series, except for critical bugs (i.e. security vulnerabilities or server crashses).We're instead focusing on getting 0.6.0 finished and out. Any reported bugs that do not fall under the afformentioned critera will instead be fixed in that release.